mirror of
https://github.com/domainaware/parsedmarc.git
synced 2026-09-21 13:18:33 +00:00


 52edca0245
A tag push ran python-tests.yml — lint, docs build, the test matrix — and
nothing else. CodeQL runs as GitHub default setup rather than from that
workflow, so release.yml never saw it, and a pull request's own CodeQL check
reports only what that diff introduces, which means an alert already open on
master passed every check a release went through.

release.yml now has a code-scanning job that build waits on, so a release
stops before it publishes anything rather than after. Everything else hangs
off build, so gating build gates the PyPI upload, the GitHub release, the
Docker image, and the docs deploy with it.

Reading the alert list is only meaningful if CodeQL has looked at the code
being released, and the tag is usually pushed moments after the commit lands
on master, while its analyses are still running. So the job first waits, up to
15 minutes, for an analysis of the tagged commit in every language CodeQL
covers. That set is read back from the analyses already published for the
default branch instead of hard-coded, so it cannot drift out of step with the
repository configuration, and a commit CodeQL never analyzed fails rather than
passing against a scan of different code.

A false positive is dismissed in the Security tab: a dismissed alert has state
"dismissed", not "open", so it stops blocking without needing an exception
here.

Co-authored-by: Sean Whalen <seanthegeek@users.noreply.github.com>
Co-authored-by: Claude Opus 5 (1M context) <noreply@anthropic.com>
parsedmarc


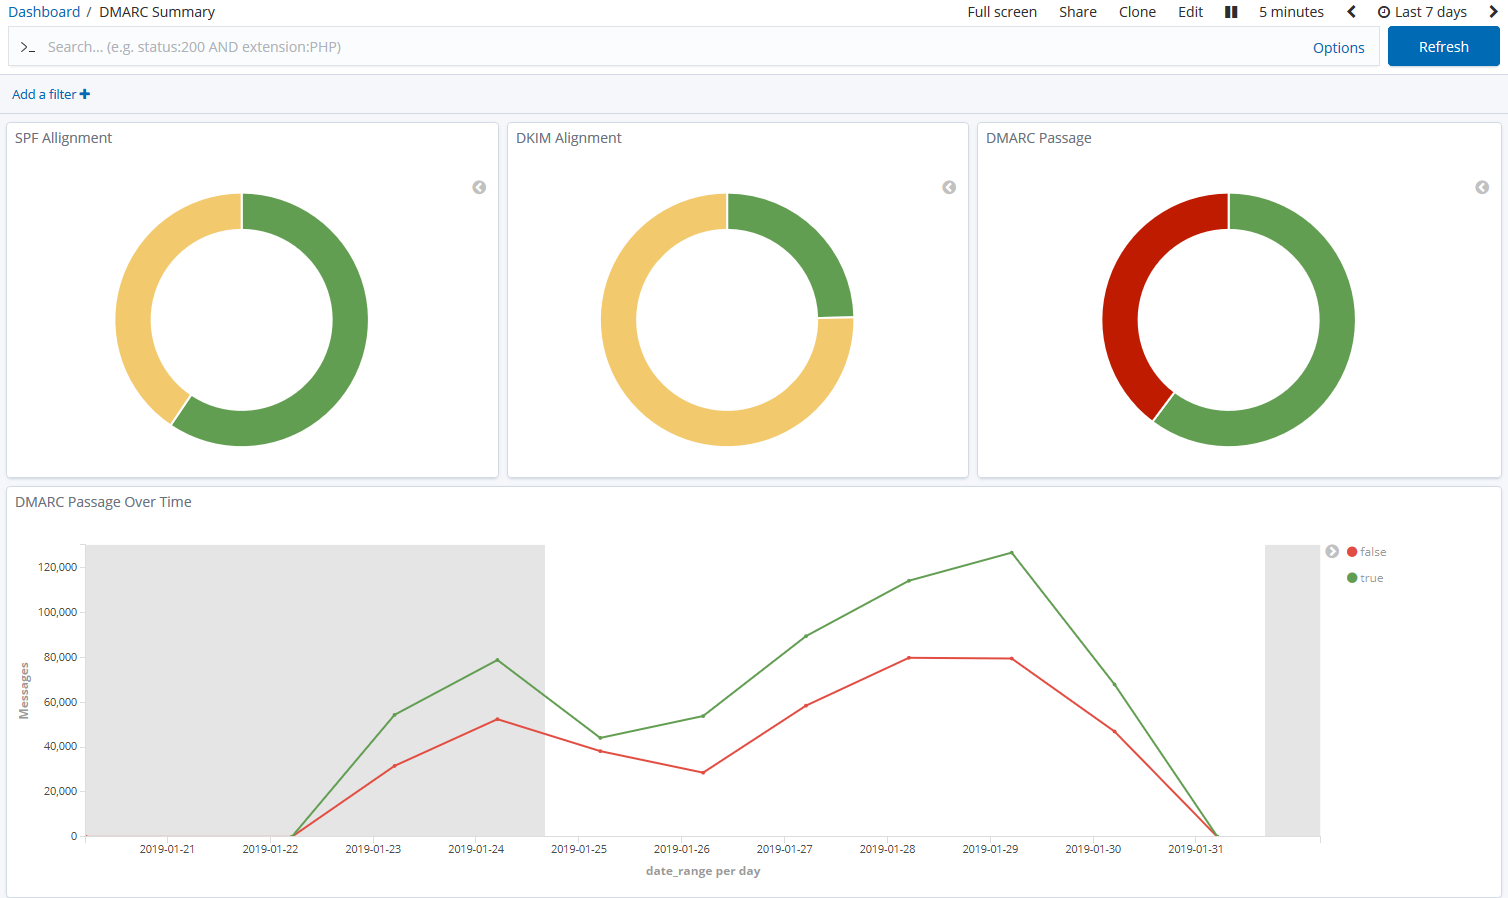
parsedmarc is a Python module and CLI utility for parsing DMARC
reports. When used with Elasticsearch and Kibana (or Splunk), or with
OpenSearch and Grafana, it works as a self-hosted open-source
alternative to commercial DMARC report processing services such as
Agari Brand Protection, Dmarcian, OnDMARC, ProofPoint Email Fraud
Defense, and Valimail.
Note
Domain-based Message Authentication, Reporting, and Conformance (DMARC) is an email authentication protocol.
Sponsors
This project is maintained by one developer. Please consider sponsoring my work if you or your organization benefit from it.
Features
- Parses aggregate/rua DMARC reports: the legacy draft and 1.0 schemas (RFC 7489) and the new RFC 9990 schema for the final DMARC standard (RFC 9989)
- Parses failure/ruf DMARC reports (RFC 6591 and RFC 9991; formerly called forensic reports)
- Parses reports from SMTP TLS Reporting (TLS-RPT, RFC 8460)
- Can parse reports from an inbox over IMAP, Microsoft Graph, or Gmail API
- Transparently handles gzip or zip compressed reports
- Consistent data structures
- Simple JSON and/or CSV output
- Optionally email the results
- Optionally send the results to Elasticsearch, OpenSearch, Splunk, or PostgreSQL, for use with premade dashboards
- Optionally send the results to Apache Kafka, Amazon S3, Azure Log Analytics (Microsoft Sentinel), a Graylog (GELF) endpoint, a syslog server, or an HTTP webhook
Python Compatibility
This project supports the following Python versions, which are either actively maintained or are the default versions for RHEL or Debian.
| Version | Supported | Reason |
|---|---|---|
| < 3.6 | ❌ | End of Life (EOL) |
| 3.6 | ❌ | Used in RHEL 8, but not supported by project dependencies |
| 3.7 | ❌ | End of Life (EOL) |
| 3.8 | ❌ | End of Life (EOL) |
| 3.9 | ❌ | Used in Debian 11 and RHEL 9, but not supported by project dependencies |
| 3.10 | ✅ | Actively maintained |
| 3.11 | ✅ | Actively maintained; supported until June 2028 (Debian 12) |
| 3.12 | ✅ | Actively maintained; supported until May 2035 (RHEL 10) |
| 3.13 | ✅ | Actively maintained; supported until June 2030 (Debian 13) |
| 3.14 | ✅ | Supported (requires imapclient>=3.1.0) |